Security Architecture & Strategy
Enterprise security architecture, standards, guardrails, and multi-year roadmaps aligned to mission and risk tolerance.
Service-Disabled Veteran-Owned Small Business
Full-spectrum cybersecurity, from strategy and architecture to operations, compliance, OT/ICS, and secure AI, plus IT consulting, for government agencies and regulated industries. Led by a U.S. Air Force veteran with nearly 25 years securing IT, OT, and cloud environments across defense, energy, and manufacturing.
Already on Microsoft 365? Get more from your license →
What we do
Enterprise security architecture, standards, guardrails, and multi-year roadmaps aligned to mission and risk tolerance.
Fractional security leadership: program scoping, priorities, budget input, and executive and board risk reporting.
Zero Trust maturity assessments, roadmaps, and phased implementation across identity, devices, network, and data.
Access governance, privileged access reviews, just-in-time access, and phishing-resistant passwordless MFA.
Cloud security architecture, CNAPP, CSPM/CWPP, SaaS posture management, and automated alert-to-ticket pipelines.
SOC design and maturity, SIEM/XDR tuning, detection engineering, playbooks and automation, threat hunting, incident response planning, and tabletop exercises.
Network segmentation, perimeter defense, firewall rule review and cleanup, secure remote access, and network architecture hardening.
KPIs and KRIs that matter, risk dashboards, and clear executive and board reporting that tie security to business outcomes.
Security awareness and behavior change, stakeholder engagement, and change management that makes new security programs stick.
Risk-based vulnerability programs, remediation governance, patch automation, and attack surface reduction.
NIST 800-53, RMF/STIG, CMMC readiness, ISO 27001, and CIS benchmarks: gap assessments and audit support.
Industrial network segmentation, secure remote access, and ICS/SCADA security controls for manufacturing and energy.
Data classification, DLP, information protection, and insider risk programs.
AI use policies, data guardrails, and risk assessments so teams adopt AI tools safely and productively.
Infrastructure and endpoint design, hardening, and modernization planning.
Security assessments
Independent, vendor-agnostic assessments that turn uncertainty into a clear, prioritized plan.
Benchmark your program against the NIST Cybersecurity Framework.
Measure maturity across identity, devices, network, applications, and data.
Find unused license value, misconfigurations, and quick wins.
Review Azure and AWS configurations, workloads, and SaaS exposure.
Assess segmentation, remote access, and ICS controls in industrial environments.
Evaluate IAM/PAM, privileged access, MFA coverage, and access reviews.
Evaluate data guardrails, AI use policies, and risk before you scale AI.
NIST 800-53, NIST 800-171, CMMC readiness, and ISO 27001 gap analysis.
Featured service
Many organizations pay for Microsoft 365 E3/E5 security features they never fully turn on. We map what you own, close the gaps, and put it to work, often before you buy another tool.
Conditional Access, PIM, and passwordless MFA. Proven: migrated 500+ apps to Entra ID, saving $1M+ a year.
DLP, information protection, and insider risk. Proven: DLP program blocking 1,500+ exfiltration attempts a month.
Unified detection, SIEM tuning, and response automation, plus Intune device compliance.
Azure posture and workload protection. Proven: automated 5,000+ monthly Azure security alerts and cut response time by 88%.
About
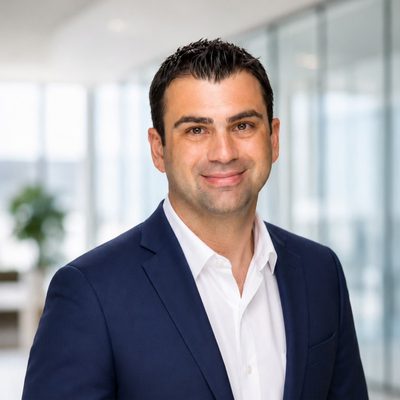
Hawkcrest Cyber was founded by Cory Zaner, a Senior Enterprise Architect specializing in security architecture and a U.S. Air Force veteran. As a Network Systems Manager and Staff Sergeant (2002–2008), Cory led a team securing satellite and UAV communications systems and was named Non-Commissioned Officer of the Year.
He then spent five years in defense, engineering DoD cyber infrastructure for ISR systems under RMF/STIG at a major aerospace and defense contractor. For more than a decade since, he has served as a lead security architect at a Fortune 500 company in the energy and chemical industry, coordinating with the CISO and cybersecurity directors across GRC, security operations, cloud security, and OT, shaping a multimillion-dollar security budget, and leading roughly 50 people through cross-functional influence. His work spans Zero Trust, identity, cloud security, OT/ICS protection, data loss prevention, incident response, and GRC for an enterprise of 10,000+ users.
Hawkcrest brings that same discipline to every engagement: clear communication, accountable execution, and security that serves the mission.
Insights
Ten countries just took down the KillSec ransomware group and seized 110 TB of stolen data. The detail that matters: investigators say KillSec used AI to build its infrastructure and pick its…
Read article →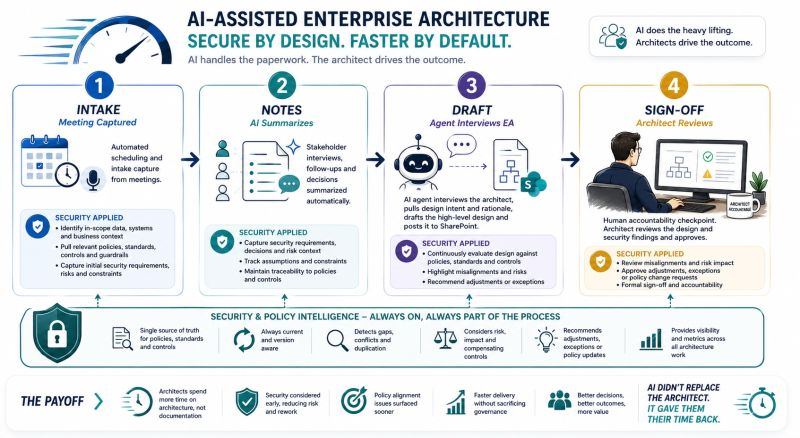
What if security architecture happened during the design — not after it? One of the biggest taxes on an enterprise architect’s time isn’t architecture. It’s documentation. So we started taking the…
Read article →
One pattern I keep seeing in security programs: We start with how to implement something before we clearly define what we should be doing and why it matters. The conversation quickly shifts to: •…
Read article →Credentials
Frameworks: NIST 800-53 Rev. 5 · RMF/STIG · ISO 27001 · CIS Level 2 · Zero Trust
For government buyers
Hawkcrest Cyber LLC
Spring, Texas
Service-Disabled Veteran-Owned (SDVOSB certification pending)
Texas VetHUB certification pending
UEI: Pending
CAGE: Pending
541512 Computer Systems Design Services
541519 Other Computer Related Services
541690 Other Scientific & Technical Consulting
541611 Administrative & General Management Consulting
Get started
Tell us about your project, contract vehicle, or security challenge.
[email protected]